

Broader Model Access and Tighter Governance Controls in 2.38
What's new in 2.38
This release broadens which models and cloud providers teams can run through Coder, including OpenAI-compatible access over Bedrock and native Claude on AWS. It also gives admins stronger, more standardized ways to govern access, from IAM roles to OAuth 2.1.
Coder Agents: New Models, Org-Wide Defaults, and Chat Management Improvements
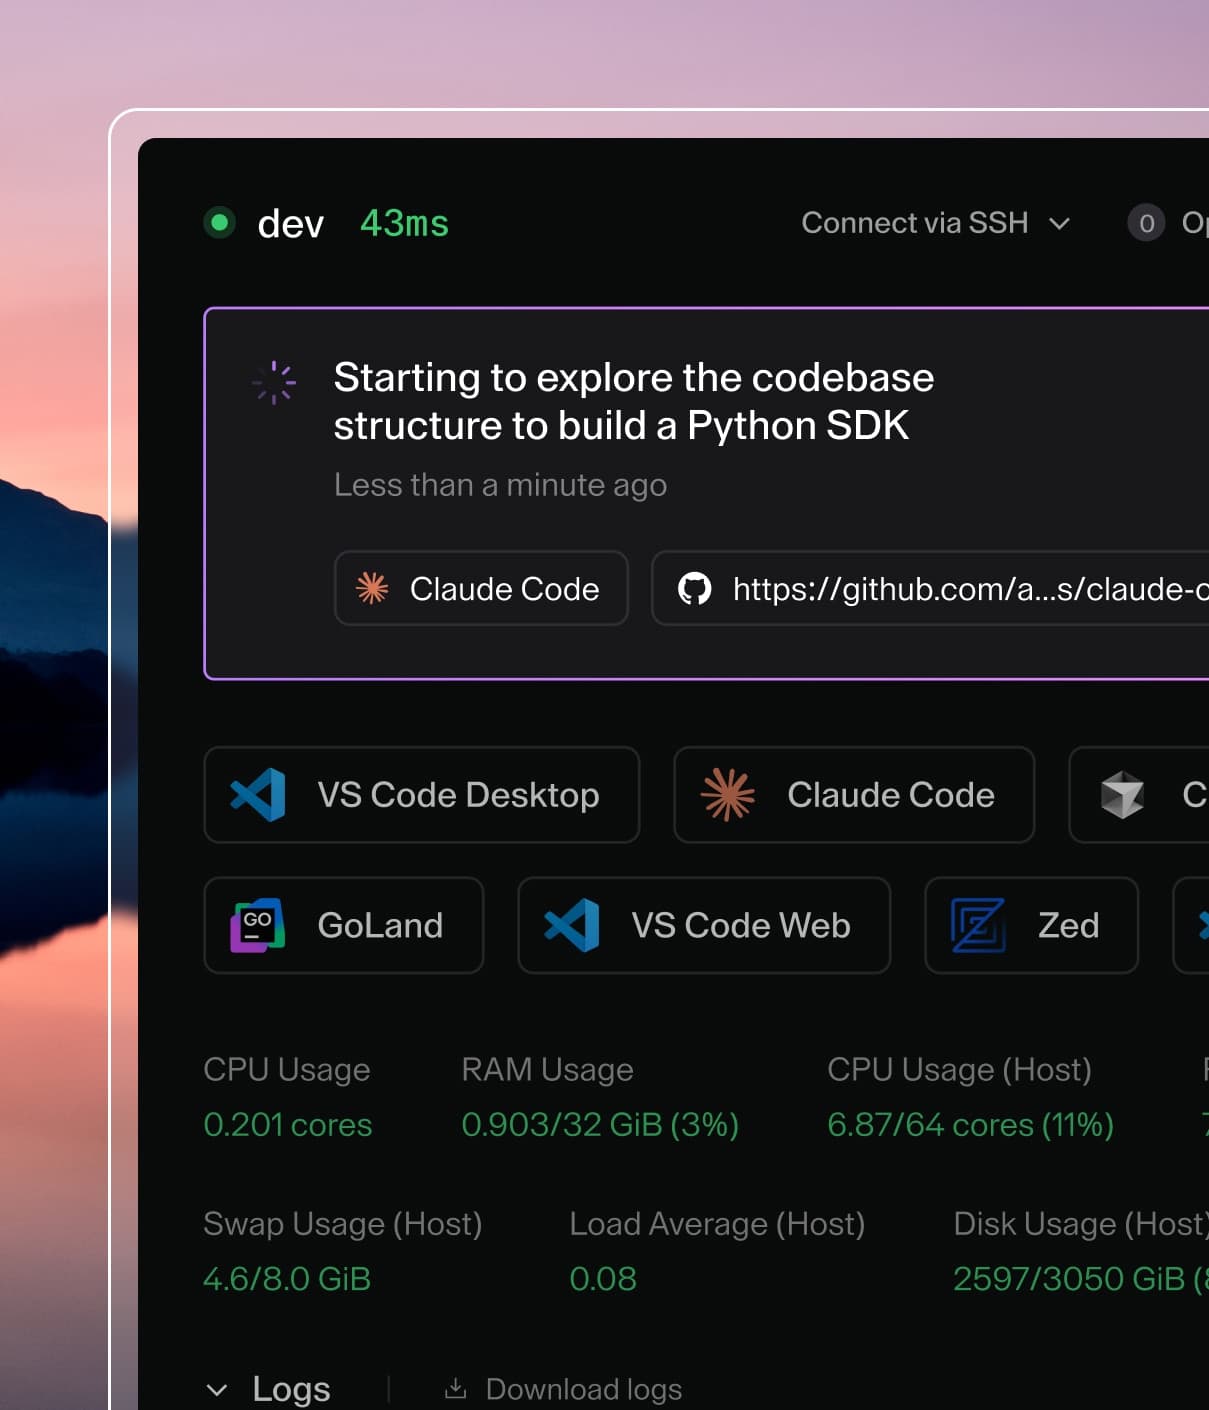
This release adds new model support with org-level defaults, streams large file uploads straight to the workspace, and reworks chat filtering and search.
- New models available with org-wide defaults: GPT-6 Sol, GPT-6 Luna, GPT-6.1 Sol, Claude Opus 5.5, and Claude Sonnet 5.5 are now supported, along with non-Anthropic models via AWS Bedrock Mantle. Admins can set an org-wide default model under AI > Coder Agents settings, so new chats use the org default instead of each user's last pick.
- Large file uploads stream to the workspace: Files outside the inline attachment allowlist (zips, datasets, tarballs, etc.) now stream directly to the workspace filesystem with no size cap, where the agent's tools can unzip, parse, and run tests on them. The model only sees a path reference, not the file bytes. This works from both existing chats and the new chat page, with the UI automatically routing attachment-compatible types inline and everything else to the workspace.
- Chat management improvements: Filter chats by status, PR status (including "no PR"), and mark chats read or unread, with a reworked sidebar featuring a dropdown filter and section switcher. Use
/clearto reset context mid-conversation, and share prompt links that prefill the composer from a URL for one-click runbooks or onboarding workflows.
AI Gateway: Support for Claude Platform on AWS
Teams that buy Claude through AWS can now send Claude Code and other Anthropic tools through Coder to Anthropic's native API on AWS, with no extra signing proxy.
- Set up in two fields: Select "Claude Platform for AWS" on an Anthropic provider, then enter a region and workspace ID.
- Authenticate without managing keys: Requests use stored Claude Platform API keys, or fall back to the gateway's ambient AWS IAM credentials via SigV4 when no key is present.
- Keep existing integrations unchanged: Coder keeps its central governance, usage attribution and auditing, and developers keep standard Anthropic model IDs and the full Messages API.
Learn more in our documentation.

Embedded NATS Pubsub for High-Availability Deployments
Coder now carries real-time events between coderd replicas over embedded NATS by default, instead of Postgres LISTEN/NOTIFY, so HA deployments can absorb traffic bursts like a wave of agents reconnecting at once.
- More headroom, no extra compute: Each coderd replica runs an embedded NATS server and meshes with the others, with automatic mutual TLS for Enterprise. The API, CLI, and dashboard are unchanged.
- Check port 6222 before upgrading (HA only): Allow TCP 6222 between all replicas in both directions. With custom relays, set
CODER_CLUSTER_HOSTor Coder falls back to Postgres pubsub. - Easy to opt out: Enable
no_nats_pubsuband restart coderd to return to Postgres pubsub. No data migration needed.
Learn more in our documentation.
Authenticate to Bedrock with IAM roles
Coder now supports role-based AWS authentication for Bedrock, so teams can move off long-lived static credentials.
- New
provider.Bedrockwith AWS SigV4 middleware: Credentials resolve via static keys, the ambient credential chain, or AssumeRole, enabling IAM-role and IRSA-based auth for workspaces. - OpenAI-compatible model access: Alongside Anthropic Messages, Coder now supports the OpenAI Chat Completions and Responses wire protocols over Bedrock's Mantle inference endpoint, extending access beyond Anthropic-only models.
- No loss of governance: Budgets, rate limits, BYOK policy, and full interception recording (prompts, tokens, tool calls) all continue to work exactly as they do today.
Learn more in our documentation.
Secure workspace access with OAuth 2.1
- Standards-based application access: Coder now officially supports OAuth 2.1, letting users connect to Coder through systems like GitHub instead of relying on a shared secret.
- Scoped app permissions: Admins can restrict an OAuth app to specific scopes, for example, limiting a GitHub app to only the actions it needs.
- Enable when you're ready: OAuth 2.1 is available behind a feature flag, so teams can turn it on and configure it for their system.
Check the integration docs for setup details and the testing steps teams should complete before upgrading.
Coder VS Code Extension v1.16.4: More Reliable Connections, Less Guesswork
This release fixes a Windows SSH permissions bug that caused "Bad owner or permissions" errors, and makes workspace updates land on the correct template version (Coder 2.36+), prompting you if an update fails. It also auto-captures debug logs on connection failure, so there's no need to reproduce the issue with debug logging on. Learn more in our documentation and view the VS Code changelog here.
Envbox updates: ARM64 build fixes and CVE remediation
Envbox is Coder's tool for running Docker-in-Docker workspaces inside a single Kubernetes pod, without needing privileged host access. Here’s what’s new in v0.6.9:
- Builds default to the host architecture: The
Makefileautomatically detects and targets the host platform, preventing mixed-architecture images when building locally. - Sysbox
checksumsare matched automatically: Envbox selects the correct Sysboxchecksumfor the target platform, eliminating checksum failures when building on ARM64 or cross-building for ARM64. - Remediated CVEs via dependency updates: Bumped Go to 1.26.6 and updated Coder, gRPC, and DataDog tracing dependencies, helping teams clear vulnerability-scanning gates on their images.
View the full envbox changelog here, and the commit comparison from the last pre-release on GitHub.
Breaking Changes
- Tasks are fully deprecated and removed in Coder v2.38. Users can stay on the v2.34 Extended Support Release during the support period.
- #29548: The experimental chat API mounts have been removed. Please use the new /api/v2 routes, which are now the only supported path.
- #28242: Deployments with MCP servers on internal networks must
allowlistthem with--mcp-allowed-private-cidrsafter upgrading, or those connections will fail. - #29283: Embedded NATS is now the default pubsub between
coderdreplicas. Before upgrading HA deployments, allow TCP port 6222 between every pair of replicas, or enable theno_nats_pubsubexperiment to stay on Postgres pubsub. Thenats_pubsubexperiment has been removed.
View the full changelog on GitHub. If you have questions or feedback, join the conversation on Discord or email us directly!